Products
Proof-carrying software you can verify yourself. Every product we ship carries its own evidence — you re-check it on your own machine, offline, without taking our word for anything.
Proven, not promised. · Every number is measured and reproducible on the shipped source.
What we ship
open core · dual licensedOne product is packaged today; the next is on the way. The discipline is the same across everything here: it demonstrates what it claims and keeps the proof, so nothing asks you to trust us.
Sealed Agent Bus
1.5.0 · pre-release
A message bus for autonomous agents where every boundary event — what crossed, when, from whom, and what the machine refused — is written into a hash-chained, signed, append-only notary log before it takes effect. A buyer can re-verify the shipped artifact offline, without trusting us. Source-available under the Business Source License 1.1 — free to read, audit and evaluate; production use needs a commercial licence.
seats: — of 4 takenfree
Zafire Bug-finder
coming soonThe entry point to verified bug-finding. Point one worker at your project — it finds real bugs, demonstrated, not guessed, shows what is there and never touches your code. Three levels, each adding a layer of proof:
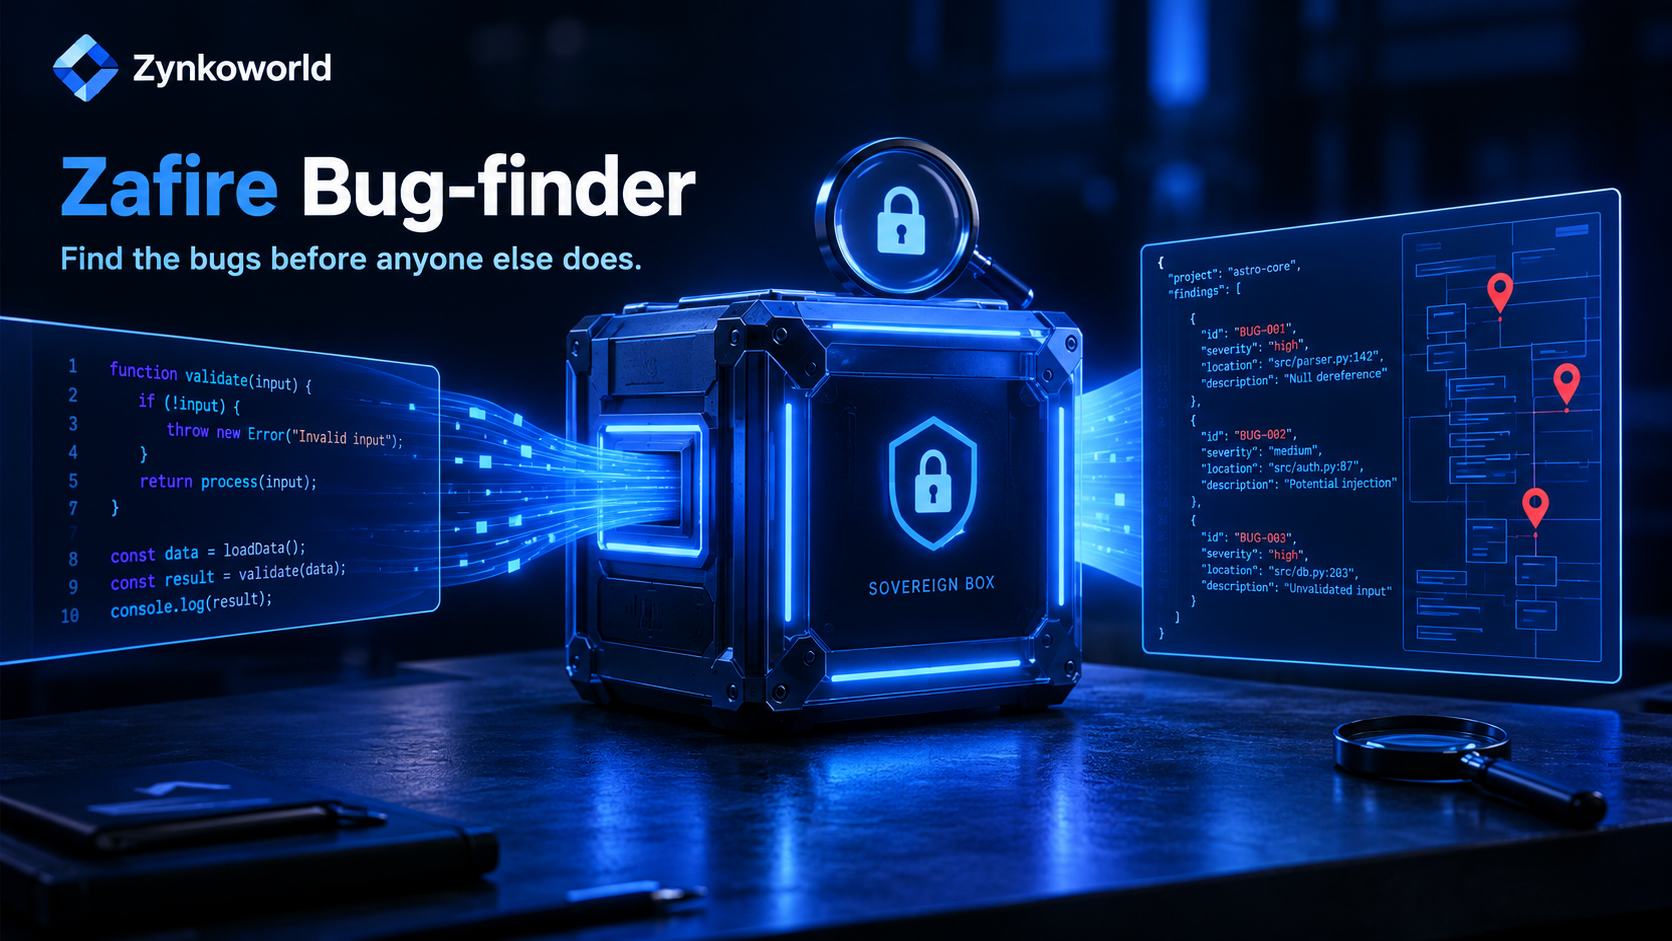
- A · Basic — read-only bug-finder; findings saved as structured JSON. Free once your machine is connected · coming soon
- B · Basic+ — adds a rule-based judge that re-checks every finding before you see it. on the roadmap
- C · Basic+ red-team — adversarial attempts to break each finding. on the roadmap
Verified Vulnerability Detector
coming soonA security scanner whose findings carry their own proof: every result is byte-lock verified by two independent arms and ships a deterministic, reproducible PoC — no AI-slop false positives. The same engine that finds real, paid bug-bounty vulnerabilities, packaged for your own code. Don't trust the scanner — verify.
Learn moreVerified Proof Layer
coming soonA drop-in verifiable-audit substrate: a hash-chained, signed, append-only notary, two independent byte-lock verification arms, and TEE attestation. Add it to any system and every event carries its own tamper-evident proof — auditable and re-checkable by anyone, offline, without trusting the operator. The trust layer under finance-grade systems: don't trust — verify.
Learn moreMore products from the Zynko line will appear here as they are packaged. Nothing is listed before it is real.
Don't trust us. Verify.
Every product on this page ships the evidence for its own claims, plus one command that re-checks them on your machine. That is the whole ethos: a proven reality, not a promise.