Verified Proof Layer
A tamper-evident audit substrate anyone can verify.
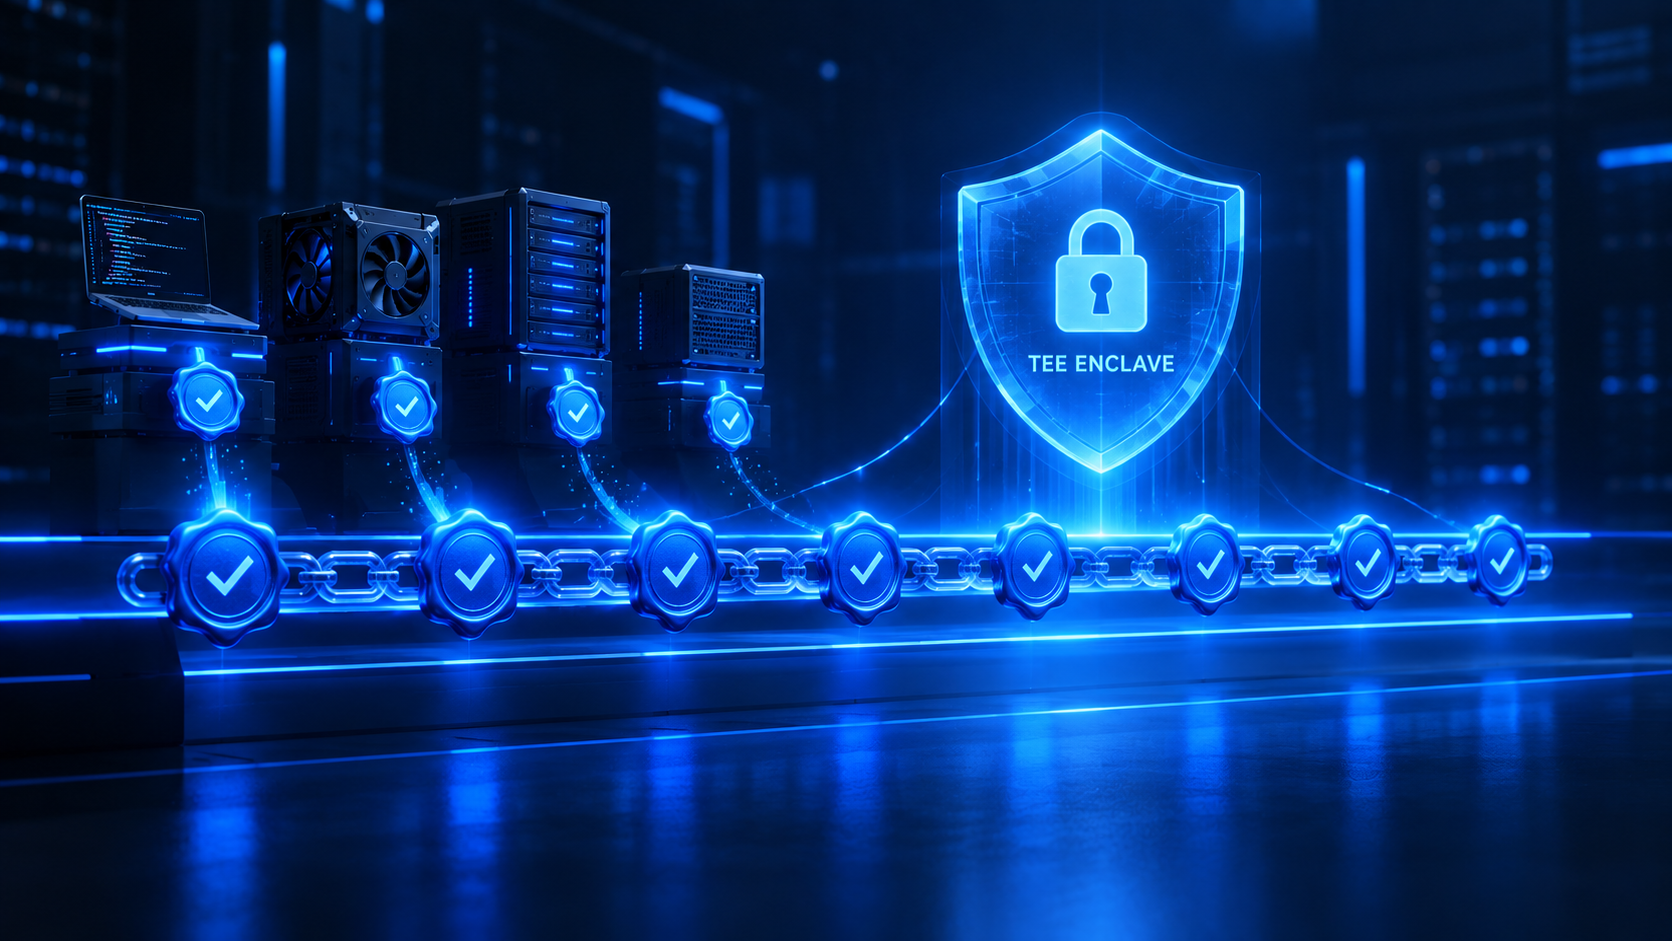
A drop-in layer that gives any system a hash-chained, signed, append-only notary, two independent byte-lock verification arms, and TEE attestation. Every event carries its own proof — re-checkable by anyone, offline, without trusting the operator.
Don't trust the operator. Verify. · The trust layer under finance-grade systems.
What it is
the proof under the systemThe proof primitives behind the Sealed Agent Bus, generalized into a layer any system can adopt — not just agents. Wire it in, and every boundary event is written to a hash-chained, signed, append-only notary before it takes effect. If the log can't be written, the operation doesn't happen: log first, act second, fail closed.
On top of the notary, two independent byte-lock arms (doer≠checker, different model families) confirm what the record claims, and a TEE-attested node lets a third party prove the check ran in a sealed enclave — not on the operator's word. The whole trail is re-verifiable offline by anyone.
What it gives you
demonstrated, not assertedHash-chained signed notary
An append-only ledger where each entry chains to the last and the head is Ed25519-signed. A deleted entry leaves a gap; nothing is silently rewritten.
Two independent verification arms
doer≠checker: a second arm from a different family byte-lock-reproduces the record. Agreement is only meaningful across families — echo is excluded by construction.
TEE attestation
The verification can run inside a confidential enclave (Intel TDX), and a remote party can check the attestation quote — proof the code ran sealed, independently verifiable.
Content-addressed transport
Payloads move as sha-256-addressed, signed chunks. Integrity and de-duplication come from the hash, not from trusting the channel.
Re-verify offline
The trail ships its own verifier: re-compute the hashes, replay the signed chain, re-check the attestation — on your machine, without trusting us.
Source-available
The layer is source-available (BSL 1.1): non-production use is free, production/commercial use requires a commercial licence. The trust engine must be visible to be trustworthy — you can audit it.
Why a proof layer, not a money network
Finance-grade systems need an auditable, tamper-evident, independently-verifiable record — that is the hard, unmet part. This is that layer: the proof under such systems, without becoming a regulated money network itself. Don't trust the operator — verify.
Licensing
source-available · commercial for productionSource-available under BSL 1.1: non-production use is free; production/commercial use requires a commercial licence. Non-production use stays free; each version converts to AGPL-3.0-or-later on 2030-09-20.
Status
honesty is part of the product- This product is in development. The primitives — the hash-chained notary, the two-arm byte-lock, and a TEE-attested enclave node — exist and run today inside the Sealed Agent Bus; the general drop-in packaging (SDK, one-command verifier, multi-node proof) is being built.
- No measured product number is claimed here yet. When it ships, every claim will be measured and reproducible on the shipped source, and the parts not yet measured will say so.
- It is a proof layer, not a value-transfer network: it records and verifies, it does not move money or run consensus for a token — that boundary is deliberate.
Coming soon. If you're building something that needs an auditable, verify-it-yourself trail, tell us the use case and we'll reach out when the drop-in layer is ready.